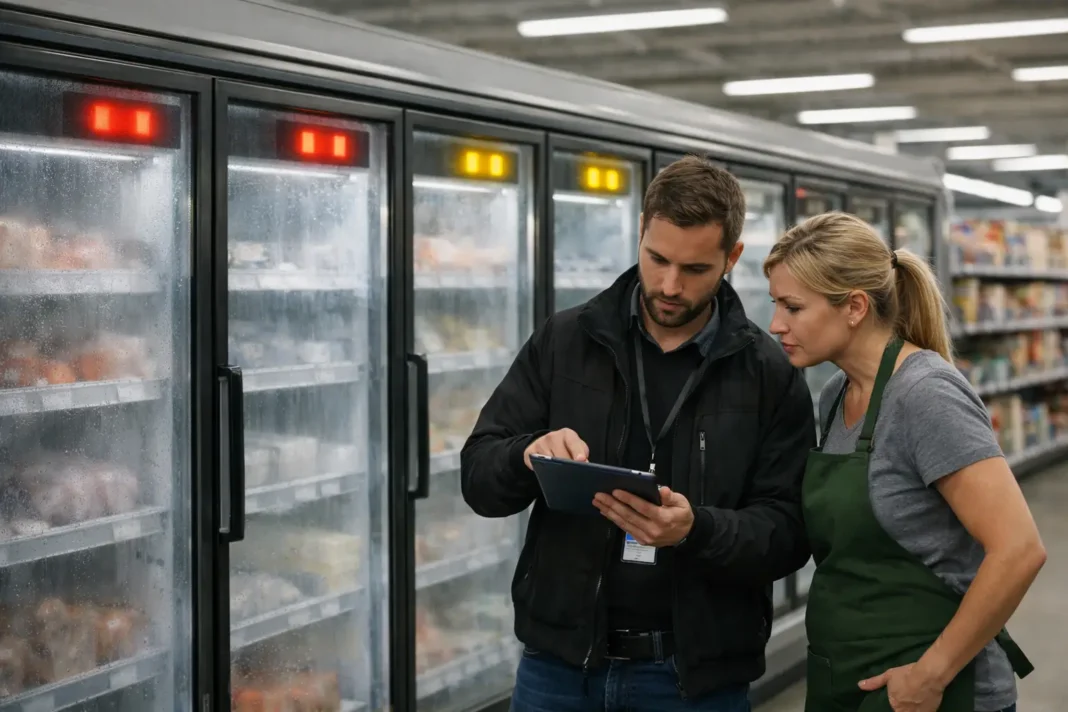

Supermarket freezers across Europe have become an unexpected example of how vulnerable everyday infrastructure can be when physical equipment is connected to the internet. In incidents stretching from Finland to Ireland, digitally controlled refrigeration units began heating rather than cooling, with some reaching 50C. Retailers were forced to discard food worth millions of euros, turning a technical breach into an immediate commercial and public-safety problem. The episode underlined a core weakness of modern retail: devices designed for efficiency, remote monitoring and lower costs can also become entry points for disruption.
The attacks sit within a broader pattern of pressure on civilian systems in Europe, where the boundary between cybercrime, sabotage and political intimidation is often difficult to define. Russian-linked hacktivists claimed responsibility for some of the supermarket disruption, but public claims do not amount to verified attribution. That uncertainty is central to so-called grey-zone activity, where disruption can spread anxiety without producing the clarity of a conventional attack. For businesses, the origin matters less in the short term than the effect: disrupted operations, spoiled goods, reputational damage and higher costs to restore service.
Transport for London offers a reminder that major disruption is not always caused by a foreign state or an advanced criminal network. A damaging hack against the capital’s transport authority was later linked to two British teenagers, showing how exposed large organisations can be even when the perpetrators are not sophisticated geopolitical actors. Retailers, transport operators and other service providers have invested heavily in protecting payment systems and logistics after costly ransomware incidents, including the disruption that forced Marks & Spencer to pause online orders in 2025. The freezer failures show that operational technology, from refrigeration to building controls, requires the same attention.
Government agencies have pushed companies to strengthen defences through warnings, guidance and training. In the United Kingdom, the National Cyber Security Centre promotes practical measures for organisations, while the European Union Agency for Cybersecurity works on resilience across the bloc. The challenge is that many connected devices were installed to improve performance, not to withstand hostile interference. Updating software, segmenting networks, monitoring unusual behaviour and rehearsing incident response are now business continuity issues rather than specialist concerns for IT departments alone.
The freezer incidents also show why cybersecurity has become a consumer-facing issue. A cyberattack on refrigeration does not merely affect data; it can remove food from shelves, create waste and erode confidence in essential services. Europe’s retailers and public authorities face a practical test: reducing the impact of future incidents before they become wider social disruptions. Resilience now depends not only on stopping intrusions, but on ensuring that essential systems can fail safely, recover quickly and keep public services functioning under pressure.